What counts as high-risk?
Art. 5, Art. 6, Annexes I and III, exceptions… classification is the first bottleneck.
AiTacora registers your AI systems, classifies them by risk level and generates only the requirements that apply to you.
The problem
Art. 5, Art. 6, Annexes I and III, exceptions… classification is the first bottleneck.
Inventories in Excel, evidence in folders and unversioned policies in emails.
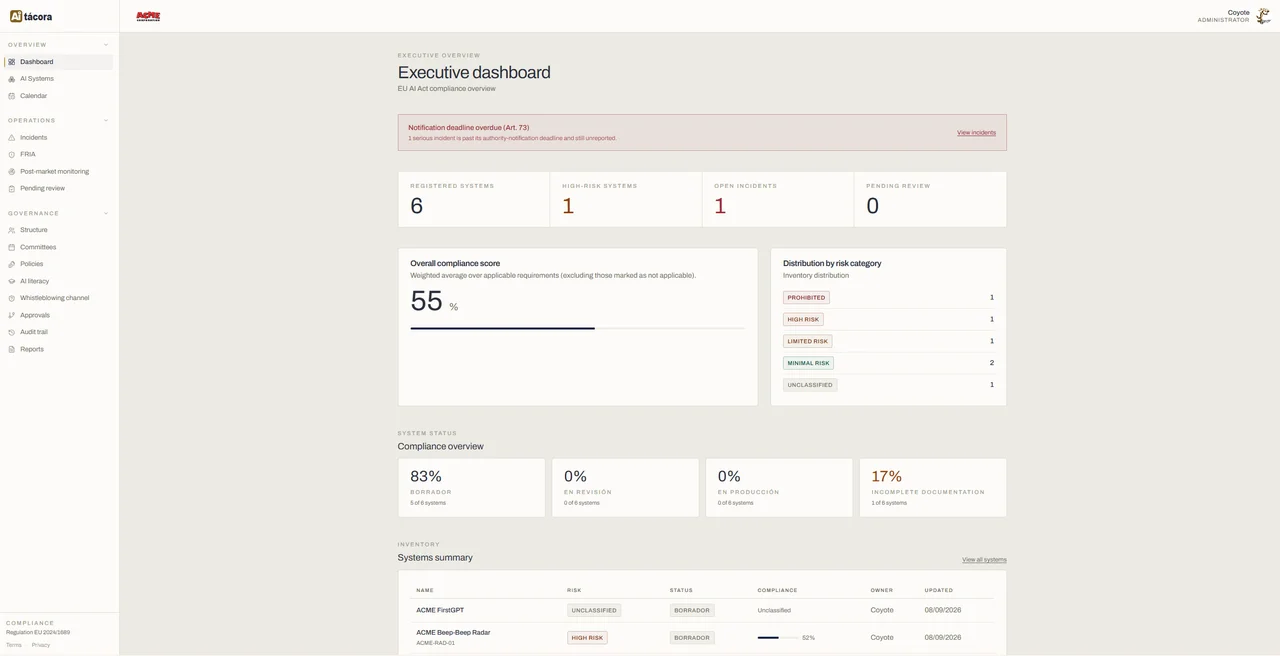
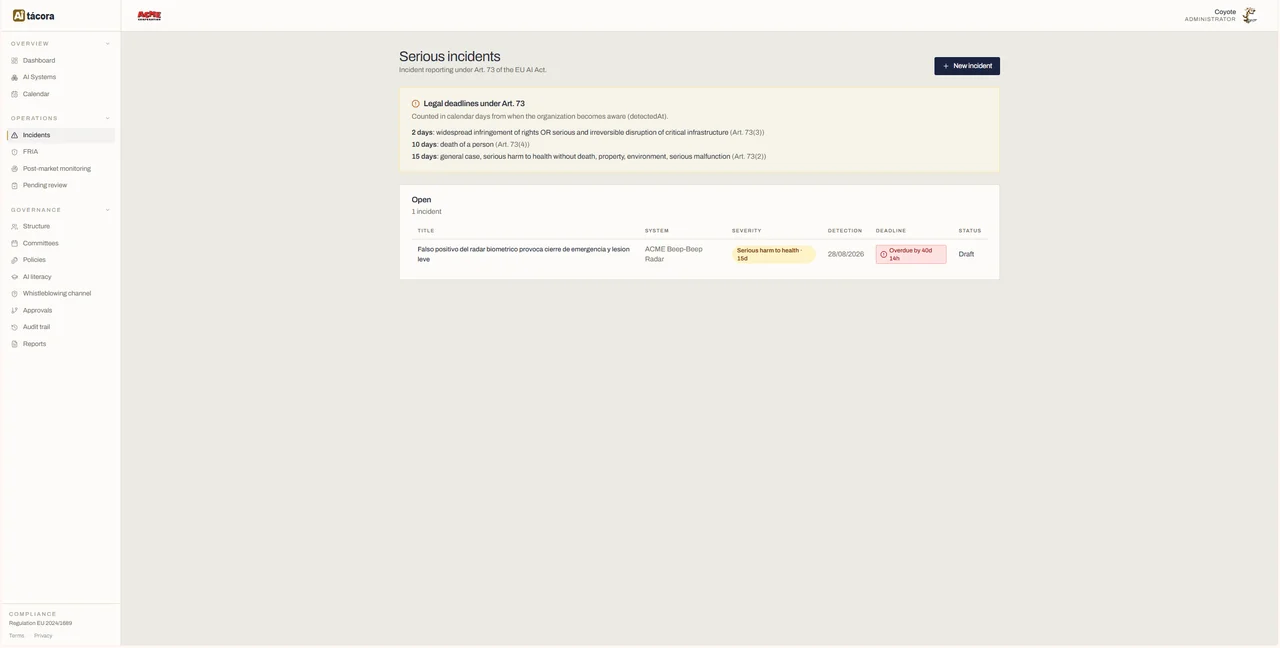
A serious incident must be reported within 2, 10 or 15 days depending on its severity (Art. 73).
The solution
Modules built article by article on the text of the Regulation.
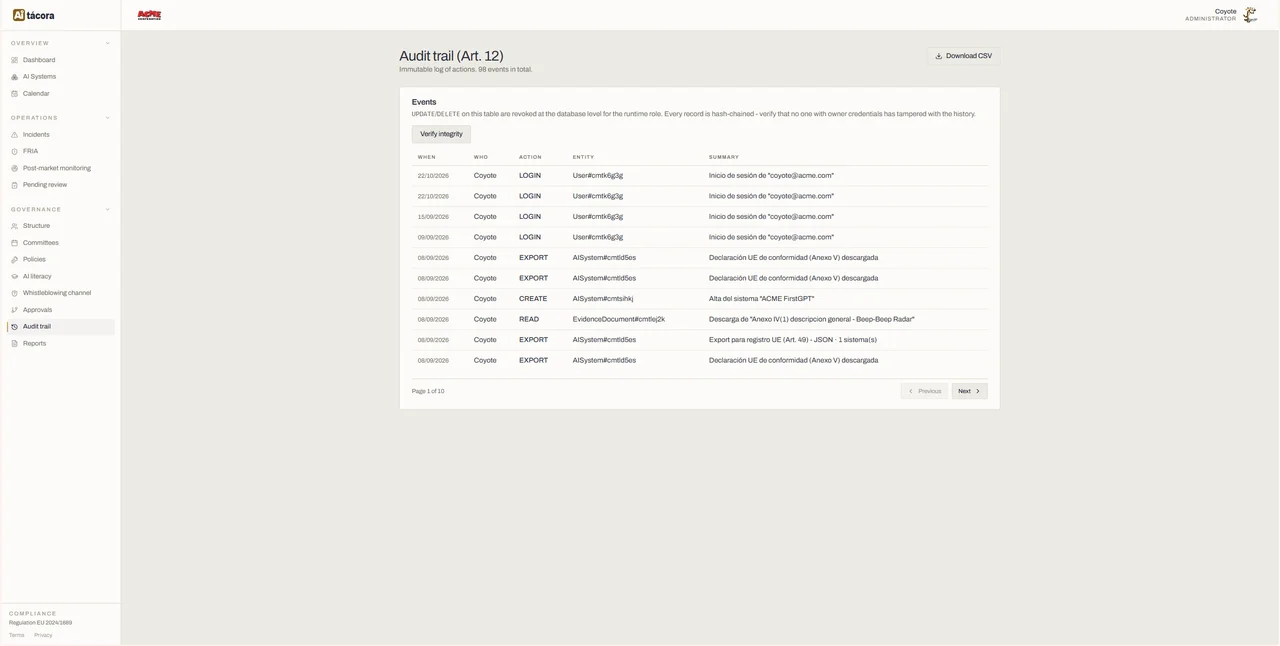
How it works
Add each system with its intended purpose, your role (provider or deployer) and its lifecycle stage.
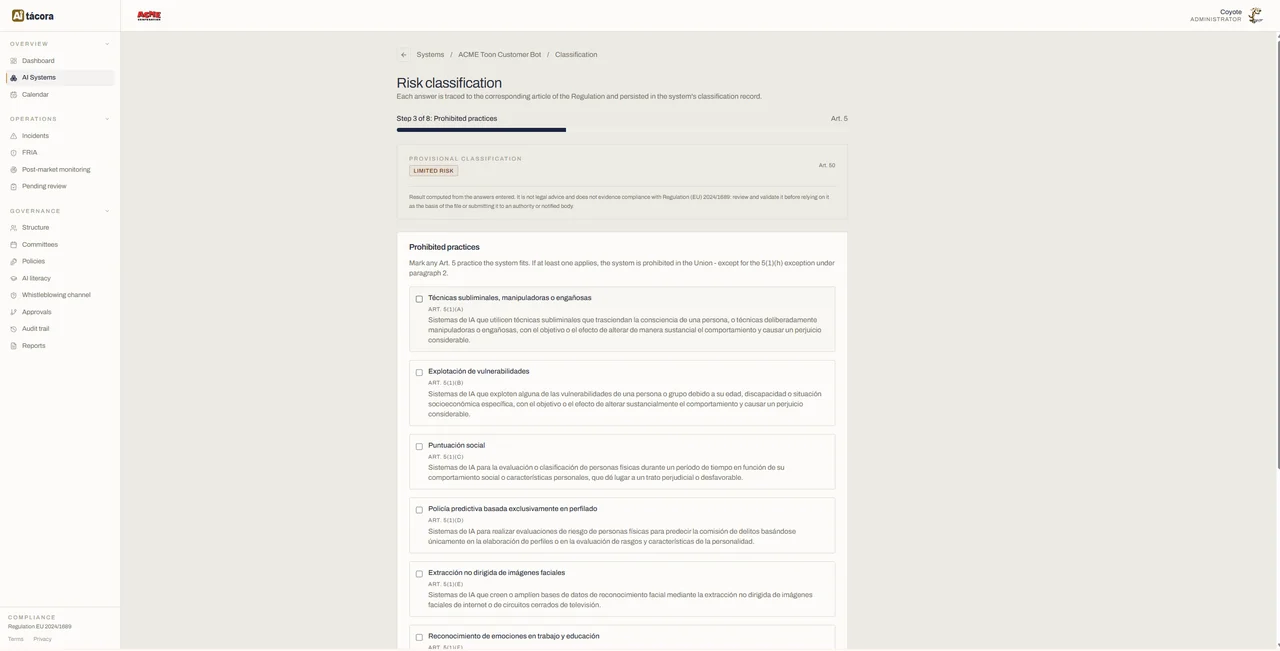
Answer the guided questions and get the risk level: prohibited, high, limited, minimal or GPAI.
Work through the generated checklist, attach evidence, manage risks and approve policies with your team.
Download the compliance report, the EU declaration of conformity and Annex VIII, and track incidents, deadlines and versions.
Who it is for
Security and trust
Your compliance file contains sensitive information. AiTacora protects it by design.
Frequently asked questions
It applies to anyone who develops, places on the market or uses AI systems in the EU, including companies outside the EU whose AI output is used here. The AiTacora wizard starts with the scope (Art. 2) precisely to rule out what falls outside it.
It depends on the obligation. The prohibitions and AI literacy have applied since February 2025, the GPAI obligations since August 2025 and the transparency obligations since August 2026. Following the Digital Omnibus, the Annex III high-risk rules apply from 2 December 2027 and the Annex I rules from 2 August 2028.
No. AiTacora organises and generates the documentation needed for the conformity assessment (Art. 43), the EU declaration of conformity (Art. 47) and registration in the EU database (Art. 49). It does not replace a notified body where one is required, nor legal advice.
Yes. The wizard distinguishes between provider and deployer, and only generates the obligations for your role. For example, the quality management system (Arts. 17-21) only appears if you are the provider of a high-risk AI system.
Hosting provider, region and encryption at rest. Each organisation is isolated from the others, and the relationship is formalised in a data processing agreement (DPA).
Request a demo. Once the contract and DPA are signed, Wildebit sets up your organisation and your administrator. From there, your team invites its users, who can sign in with email and password or with their Microsoft account.
Request a demo
Tell us which AI systems you use and we will show you AiTacora with a case similar to yours.
Prefer to email us? info@wildebit.com
We will reply within 1 business day.